Policy & Regulation
-
 Getty Images
Cambium Networks slashes workforce, courts buyers
The fixed wireless access provider laid off more than half of its employees amid accounting issues and market competition.
By James Anderson • Sept. 14, 2026 -
 Getty Images
TPx butts heads with Arista over post-bankruptcy VeloCloud support
The two parties agreed to enter mediation to resolve a lawsuit that erupted last month.
By Kelly Teal • Sept. 10, 2026 -
 Getty Images
N-able alerts MSPs to critical platform vulnerabilities
The vendor released patches for N-central remote monitoring and management servers after researchers discovered attack vectors over Labor Day weekend.
By Matt Ashare • Sept. 8, 2026 -
 Getty Images
With its bankruptcy plan approved, TPx plans new investments
CEO Shaun Andrews said his team is leaning into APIs and tools to make the company “the easiest MSP for the channel to work with.”
By James Anderson • Sept. 4, 2026 -
 Getty Images
Tech advisors move to police themselves before the FCC does
Technology Channel Sales Professionals has drafted a code of ethics and plans a Q4 launch of its new certification program.
By James Anderson • Aug. 31, 2026 -
 Permission granted by Impartner
Impartner takes a crack at streamlining channel transactions
The PRM platform added self-service deal orchestration capabilities that give resellers and distributors more control of routine sales.
By Kelly Teal • Aug. 28, 2026 -
Getty Images
TPx cancels bankruptcy auction with no qualified bids
The managed service provider turned to creditors for relief from a $1.1 billion debt.
By James Anderson • Updated Aug. 18, 2026 -
 pigphoto/iStock/Getty Images Plus via Getty Images
Civil-society initiative pays channel firms to protect rural water systems
DEF CON Franklin tapped a mix of cybersecurity vendors and partners to provide threat intelligence and response to utilities after a series of Iran-linked attacks.
By Eric Geller • Aug. 10, 2026 -
 Getty Images
Opinion
MSPs are leaving email signature compliance money on the table
A stale disclaimer after a merger is a small problem until a regulator asks about it. Regional MSPs are best placed to spot that, and to charge for fixing it.
By Larry Lodge • Aug. 6, 2026 -
 MF3d via Getty Images
Tech industry alliance proposes AI agent safety reporting program
The information-sharing exchange is designed to widely share lessons learned from agentic AI security incidents.
By Eric Geller • Aug. 4, 2026 -
 Getty Images
N-able rocked by managed services platform breach
The vendor urged customers to quickly patch vulnerabilities discovered over the weekend in its flagship N-central console.
By Matt Ashare • Updated Aug. 4, 2026 -
 Permission granted by Westcon-Comstor
Westcon-Comstor wants to slash emissions in half by 2030, and it needs partners’ help
After cutting direct emissions by 42% since 2022, the distributor faces the harder challenge of reducing emissions across its supply chain.
By Nidhi Sharma • July 31, 2026 -
 Permission granted by Josh Hobein
Coalition creates insurance collaboration with MSPs
The firm is carving out a niche between big-name insurance carriers and security vendors that provide breach warranties.
By James Anderson • July 29, 2026 -
 Andrew Harnik via Getty Images
CMMC phase 2 suspended, but certified MSPs say it was worth it
The DoD's decision is a boon for IT service providers that have yet to comply with the newest Cybersecurity Maturity Model Certification requirements.
By James Anderson • July 16, 2026 -
 Getty Images
US launches vulnerability clearinghouse amid AI-fueled surge in flaws
The Trump administration hopes the program will accelerate the discovery and remediation of technical problems before hackers exploit them.
By Eric Geller • July 15, 2026 -
 Getty Images
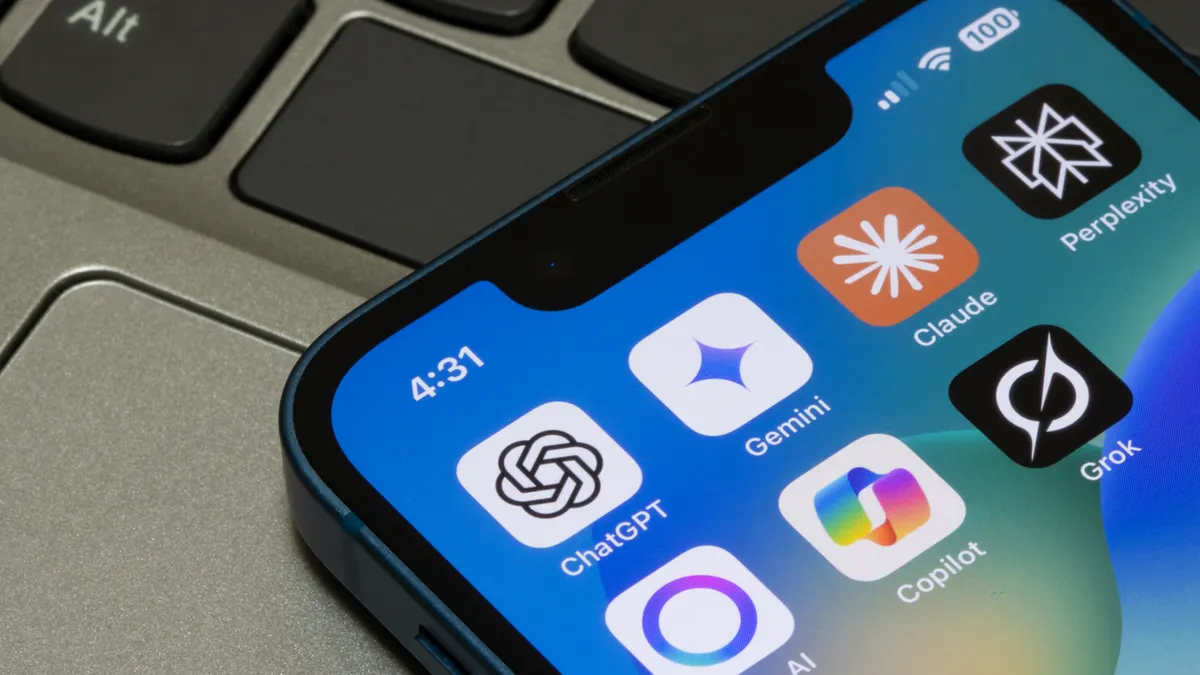
Shadow AI starts at the top
Senior leaders are disproportionately responsible for the spread of the unapproved tools, according to TrustedTech.
By Kelly Teal • July 14, 2026 -
 Permission granted by Cisco
Sponsored by Cisco
Compliance is a competitive advantage for MSPs
Compliance pressure is intensifying and expectations are getting firmer. Self-assertion is no longer enough.
July 6, 2026 -
Getty Images
TPx keeps paying commissions as it hunts a bankruptcy buyer
One partner warned of clawbacks and a wait of up to four months for clarity on who the restructuring plan considers essential.
By James Anderson • July 2, 2026 -
 Getty Images
Vulnerability exploits push channel to fortify credential defenses
Partners should heed the customer call for patch prioritization, cyber resilience and AI governance, Verizon’s channel chief said.
By Kelly Teal • June 12, 2026 -
 Eric Geller/Channel Dive
Deep Dive
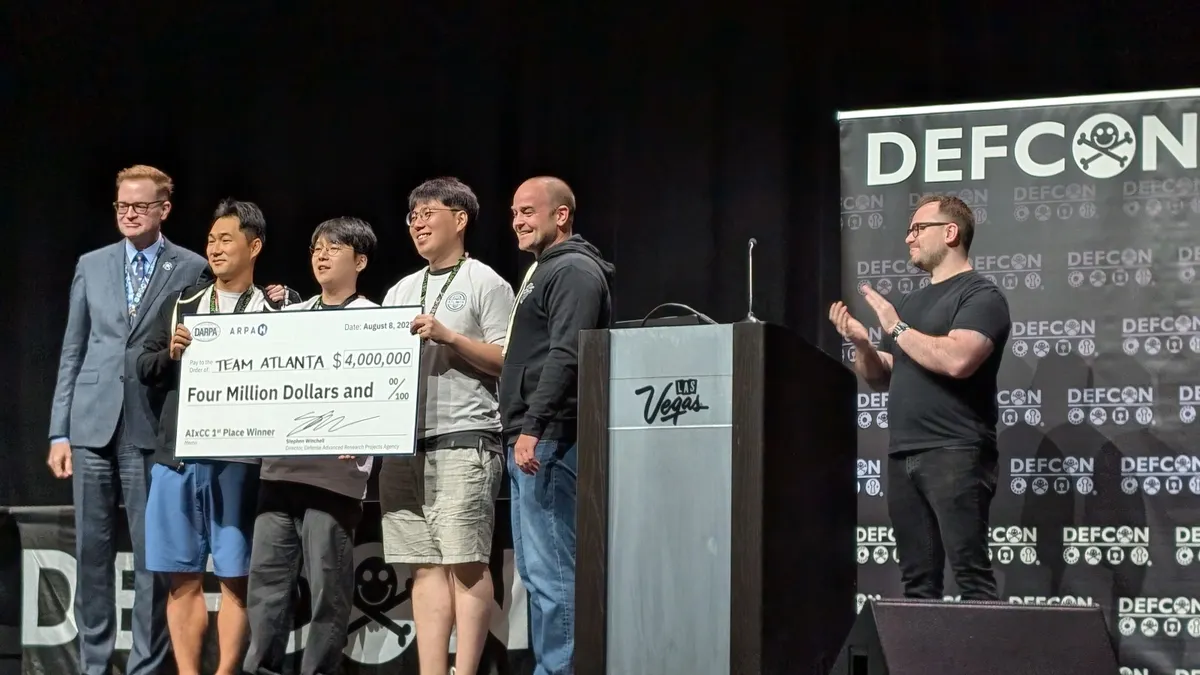
How a government contest launched a revolution in AI-based bug hunting
Security researchers have spent months honing AI systems that can find and fix serious vulnerabilities. Critical infrastructure everywhere could benefit.
By Eric Geller • May 22, 2026 -
 Sean Gallup / Staff via Getty Images
Microsoft runs afoul of UK regulators again
The Competition and Markets Authority opened an antitrust investigation into Microsoft’s business software ecosystem on Thursday.
By Matt Ashare • May 14, 2026 -
 Justin Sullivan via Getty Images
Deep Dive
New cybersecurity industry coalition aims to lead US critical infrastructure protection
The new Alliance for Critical Infrastructure’s biggest goal: changing how the nation plans for a major cybersecurity crisis.
By Eric Geller • May 14, 2026 -
 Getty Images
CISA adds Microsoft, ConnectWise vulnerabilities to active exploitation catalog
Russia has used one of the flaws, security experts said, while North Korea has used the other.
By Eric Geller • April 30, 2026 -
 tadamichi via Getty Images
Vulnerability exploitation surges often precede disclosure, offering possible early warnings
Organizations can get ahead of major flaws with the right threat intelligence, according to a new report.
By Eric Geller • April 20, 2026 -
Permission granted by Cisco
Sponsored by Cisco
Compliance is a competitive advantage for MSPs
Compliance pressure is intensifying, and expectations are getting firmer. Self-assertion is no longer enough.
April 20, 2026